Falco runtime detection to host investigation
A Falco credential-search event brings signed host evidence in under a second, and Claude traces the whole process chain with no shell access.
The scenario
Two identical web servers, web-1 and web-2, and a database host labelled as holding card data ran in AWS, with Falco on the web servers using its default rules. We planted a harmless stand-in for a credential hunt on web-1: a script in a hidden directory under /dev/shm searched for SSH private keys and AWS credentials, opened /etc/shadow without reading it, then renamed itself to look like a kernel thread and slept.
The alert
Falco raised five events on web-1 from four rules. Falcosidekick's standard webhook output posted them to the Secronyx alert bridge with a key that can post events and nothing else, and the bridge ran a playbook for the private-key search rule and logged the rest.
At a glance
Falco flags a private-key and credential search on web-1
Falcosidekick posts the event to the Secronyx alert bridge
The bridge runs a credential-access playbook of 8 read-only checks
web-1 signs every result in about a quarter of a second
Claude follows up through Secronyx, comparing web-1 with web-2
Claude reports a likely compromise and changes nothing
What Secronyx gathered, and how it was restricted
What it gathered from the host
- The full process chain, from what launched it to the running program and its working directory
- Which user each process ran as, and whether a login session was involved
- Whether the program is still running, and the images and memory mappings behind it
- Open sockets, cron jobs, timers and startup items
- The same checks on the twin host, for comparison
How it was restricted
- Read-only checks: no check returns the contents of arbitrary files, and none changes the host
- Auth logs, shell history and SSH keys need a scope this policy does not give the AI, so Claude could not read them
- A label policy decides what each caller may see; the card-data host is reserved for the security team
- Each host checks a single-use pass signed by the commander and writes every call to its own tamper-evident audit log
- Claude had one tool, the commander: no shell, no file access and no Falco access beyond the events in its first prompt
What the AI concluded
Claude's verdict was likely compromise on web-1, medium confidence. It named the full process chain from the AWS Systems Manager document worker to the disguised program, found it ran as root with no login session, was still alive minutes later disguised as a kernel thread, held no sockets and left no scheduled jobs, and that web-2 has none of this. It concluded that the real scope is in AWS, not on web-1, and that only CloudTrail could tell whether this was an approved exercise.
The proof
Figures from the recorded run, as reported in the walkthrough.
< 1 s
from the Falco event to signed host evidence
35 calls
made by Claude, all to Secronyx
18 of 18
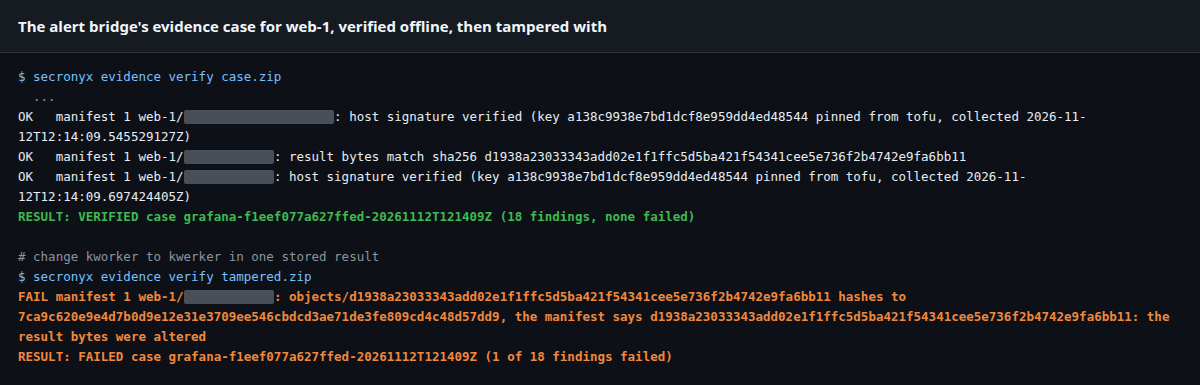
signed findings verified offline; changing one letter makes verification fail
1 playbook
for one attack: the other rules' events were logged and ignored
See every step
The walkthrough has the setup, the full story with screenshots, the evidence and how to run it yourself.
Product names belong to their owners and are used only to say what each demo connects to. Secronyx is not affiliated with, sponsored or endorsed by them.