Caddy
See which hosts and ports Caddy serves, where each site proxies, and which reverse proxy upstreams Caddy has marked unhealthy, from its admin API on this host with read-only requests. This plugin is in the next Secronyx release; the current download does not include it yet.
What it answers
Questions an on-call engineer asks, which an AI client can answer with this plugin.
- Which reverse proxy upstreams has Caddy marked unhealthy?
- Why does Caddy answer 502 Bad Gateway for this site?
- Which hosts and ports does Caddy serve, and where does each site proxy?
- How many requests are in flight to each backend, and which ones are failing?
- Is automatic HTTPS turned off on any server?
What it returns
Each of the plugin's read-only tools, described in words.
- Caddy HTTP servers in the running config - listen addresses, hosts matched, route count, handlers, upstreams proxied to, automatic HTTPS and timeouts; never handler settings
- Caddy reverse proxy upstreams, one row per upstream - its dial address, whether Caddy considers it healthy, the requests in flight to it and its recent failures counted by passive health checks
At a glance
- Plugin
- caddy 1.0.0
- Publisher
- levantar
- Platforms
- Linux, Windows, macOS
Tested on
- Caddy 2.8.4 and 2.10.2 on Linux (Ubuntu 24.04, Docker), test lab
- Caddy 2.8.4 on macOS (official release), test lab
- Caddy 2.8.4 on Windows Server 2022 (official release), test lab
How it logs in
Without an explicit choice, install tries the methods that need no secret first, in this order.
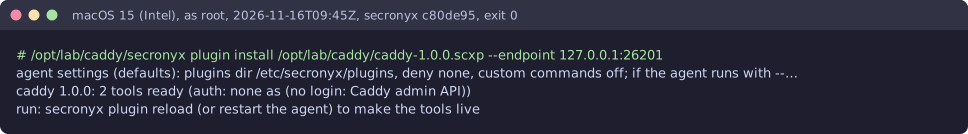
- No login (a local endpoint)
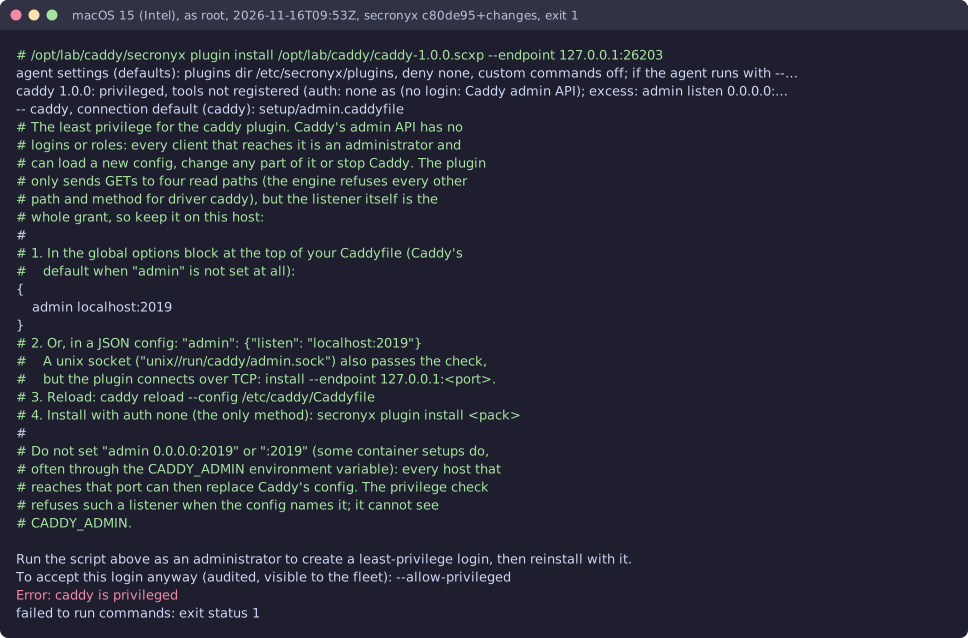
Least privilege
The setup file in the pack. This plugin needs no password and creates no login: the file says what it needs on the host and how to keep that to the minimum.
See it run
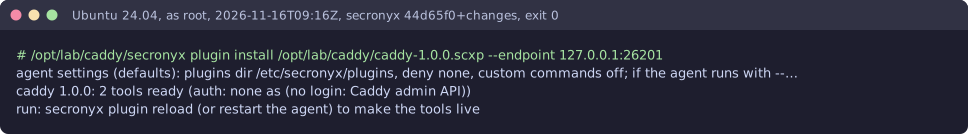
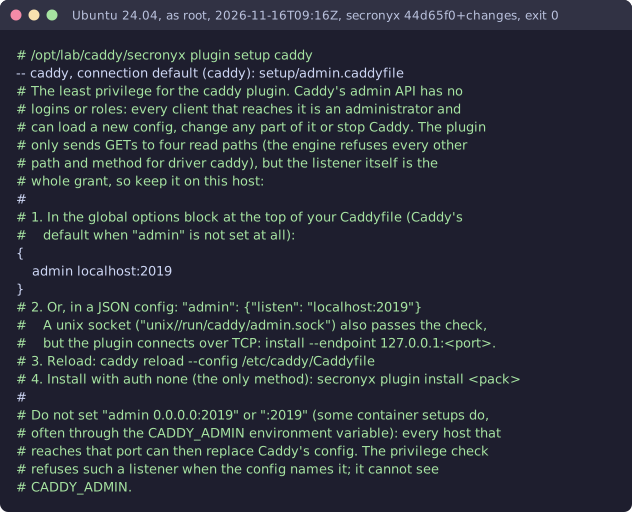
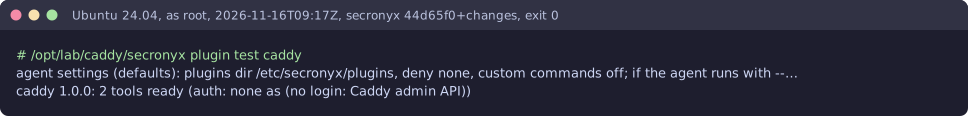
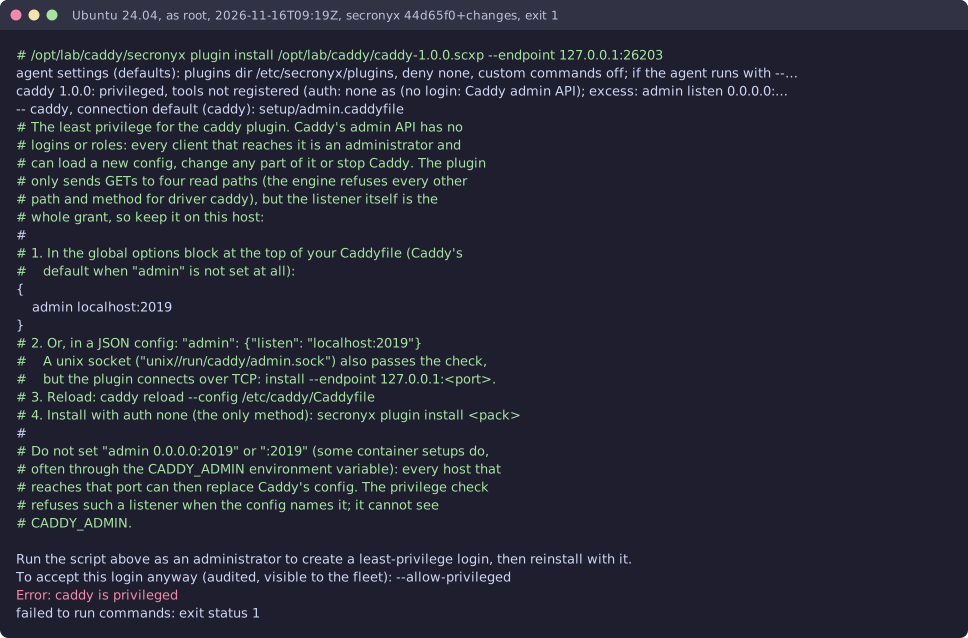
Read-only, in layers
Every request is a GET or HEAD to the endpoint the operator configured, on a path fixed in the signed pack. Redirects are not followed, and requests known to change state are refused.
These controls narrow what the plugin can do; none of them is a guarantee on its own. An administrator can still accept a more powerful login on purpose (audited and shown in status), root or Administrator on the host can replace the agent, and the plugin can read whatever its login can see.