Nomad
See which client nodes are ready, draining or down, each job's status and allocation counts, which allocations failed and how, and why a pending job cannot be placed, with a read-only ACL token. This plugin is in the next Secronyx release; the current download does not include it yet.
What it answers
Questions an on-call engineer asks, which an AI client can answer with this plugin.
- Which client nodes are down, draining or not eligible for scheduling?
- Which jobs are pending, and how many of their allocations are queued, running or failed?
- Which allocations failed, on which node, and was it an exit code, an out-of-memory kill or a failed download?
- Why can this job not be placed - a constraint, a node class, or exhausted memory, CPU or quota?
What it returns
Each of the plugin's read-only tools, described in words.
- Nomad client nodes (the first 1000) with name, datacenter, node pool and class, address, status (initializing, ready, down, disconnected), scheduling eligibility, drain and version
- Nomad jobs (the first 1000) with namespace, type, status (pending, running, dead), stopped or not, and their allocation counts - queued, starting, running, failed, complete, lost, unknown
- The 100 newest failed Nomad allocations with job, task group, node, the failed tasks, restarts, each failed task's last three event types, and the last exit's code, signal and OOM kill
- Why Nomad cannot place jobs - per task group of each blocked evaluation (newest 200), the nodes evaluated, filtered and exhausted, the filtering constraints and classes, and exhausted resources
At a glance
- Plugin
- nomad 1.0.0
- Publisher
- levantar
- Platforms
- Linux, Windows, macOS
Tested on
- Nomad 1.8.4 on Linux (Ubuntu 24.04, Docker), test lab
- Nomad 1.8.4 on macOS (official release), test lab
- Nomad 1.8.4 on Windows Server 2022 (official release), test lab
How it logs in
Without an explicit choice, install tries the methods that need no secret first, in this order.
- A bearer token
- A client certificate
- No login (a local endpoint)
The least-privilege login
The setup file in the pack. secronyx plugin setup nomad prints it; an administrator applies it by hand.
See it run
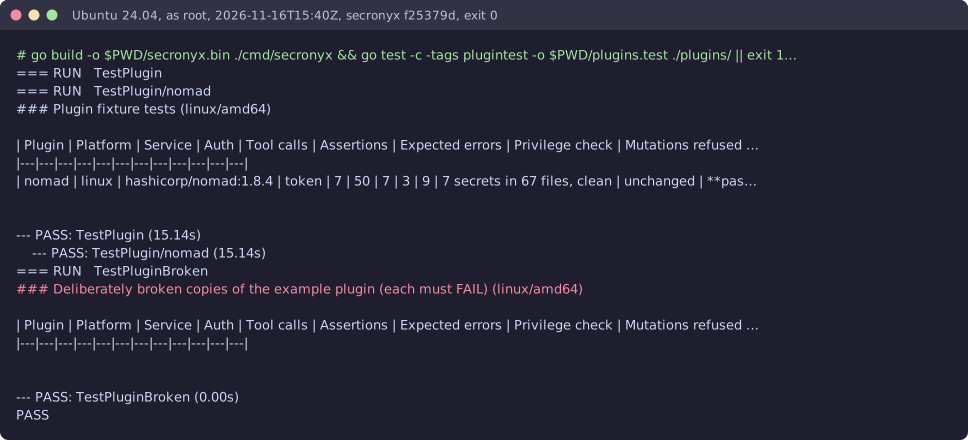
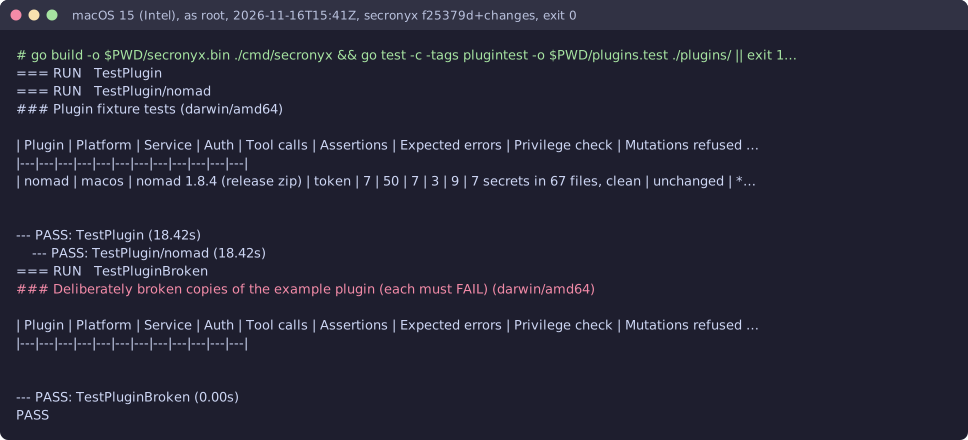
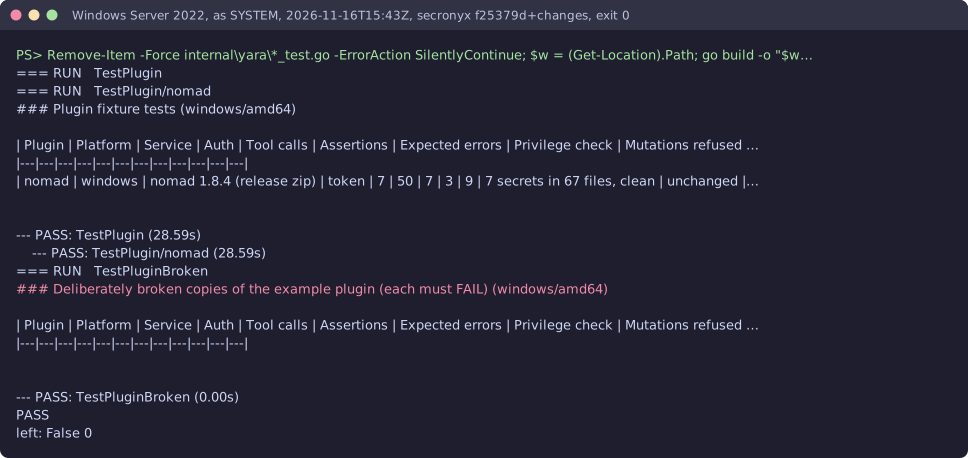
Read-only, in layers
Every request is a GET or HEAD to the endpoint the operator configured, on a path fixed in the signed pack. Redirects are not followed, and requests known to change state are refused.
These controls narrow what the plugin can do; none of them is a guarantee on its own. An administrator can still accept a more powerful login on purpose (audited and shown in status), root or Administrator on the host can replace the agent, and the plugin can read whatever its login can see.